CYBERSECURITY, DIGITAL RISK & BUSINESS RESILIENCE
Reduce digital risk before it becomes a business interruption.
EmberNova Digital helps businesses identify digital weaknesses, strengthen access and ownership, improve recovery readiness, and build practical safeguards around the systems they depend on every day.
The goal is not to turn the business into a security department. It is to reduce avoidable risk, improve visibility, and make the organization harder to disrupt.
2026 Best of Florida® Winner · Business Consulting Firms
Florida-based · Serving businesses nationwide · Licensed & Insured · Confidential by design
DIGITAL RISK IS BUSINESS RISK
Most businesses do not need more fear. They need a clearer picture of what could actually go wrong.
Digital risk often builds quietly.
A former employee still has access. A domain is controlled through someone’s personal account. Backups exist but have never been tested. Email security is incomplete. Critical systems rely on one administrator. Vendors have accumulated permissions no one has reviewed.
None of those problems necessarily look urgent until something changes.
EmberNova Digital helps identify those weak points before they become an outage, account loss, data exposure, or recovery project.
This may be the right conversation when:
- No one is completely sure who has access to critical business systems
- Domains, hosting, email, cloud accounts, or software ownership are unclear
- Former employees, vendors, or contractors may still have permissions
- Multi-factor authentication and account recovery are inconsistent
- Backups exist, but recovery has never been tested
- The business relies heavily on one person to understand its digital environment
- Leadership wants a practical risk review without buying an enterprise security program
- Growth, succession, acquisition, compliance requirements, or insurance are increasing the need for stronger controls
The most useful cybersecurity work starts by understanding what the business actually depends on.
PRACTICAL SECURITY
Protect the systems that matter without making the business impossible to operate.
Security controls only work when people can realistically use them.
EmberNova Digital takes an operational approach to cybersecurity by looking at the business environment, the people who use it, the systems that matter most, and the consequences if access, data, or availability are disrupted.
The objective is to strengthen the highest-value areas first and build controls the organization can actually maintain.
Resilience means reducing the chance of failure and improving the business’s ability to recover from one.
Reduce the likelihood of an incident
Stronger access controls, MFA, permissions, account ownership, email protection, software hygiene, vendor access, and security-conscious configuration.
Reduce the impact when something goes wrong
Backups, recovery access, documentation, escalation paths, ownership clarity, continuity planning, and tested recovery procedures.
WHAT WE HELP WITH
Strengthen the parts of the digital environment that create the most business risk.
Every environment is different. The work may begin with a focused security assessment, an access problem, a fragile digital setup, or a broader review of how the business protects and recovers its critical systems.
Digital Risk Assessments
Review critical systems, people, accounts, access, ownership, security practices, dependencies, security tools, and recovery readiness to identify meaningful business risk and practical priorities.
Identity, Access & Account Security
Strengthen passwords, MFA, administrator access, user roles, account recovery, email security, vendor permissions, and employee access throughout the user lifecycle.
Security Technology & Monitoring
Review the security tools already in place, identify gaps or unnecessary overlap, and help establish practical monitoring of endpoint protection, email security, backups, alerts, account activity, and other critical security platforms.
Backup, Recovery & Business Continuity
Evaluate backups, restoration capability, recovery access, critical dependencies, continuity plans, and what the business would actually do if important systems became unavailable.
Digital Ownership & Resilience
Clarify control of domains, hosting, cloud platforms, software, credentials, administrative accounts, and other critical digital assets so the business is not dependent on one person or vendor.
Security Policies, Awareness & Operational Practices
Establish practical standards for passwords, MFA, software updates, devices, vendors, employee transitions, incident reporting, recovery, and everyday security behavior.
Not sure which security gaps matter most?
EmberNova Digital can review your digital environment, identify the highest-risk weaknesses, and help prioritize practical improvements around access, ownership, recovery, and resilience.
FROM RISK TO RESILIENCE
Understand what matters, strengthen the weak points, and improve the business’s ability to recover.
Cybersecurity work is most useful when it is tied to the systems the business actually depends on.
EmberNova Digital starts by identifying the environment, access, ownership, critical dependencies, and recovery realities. From there, we prioritize practical improvements based on business impact rather than treating every technical issue as equally urgent.
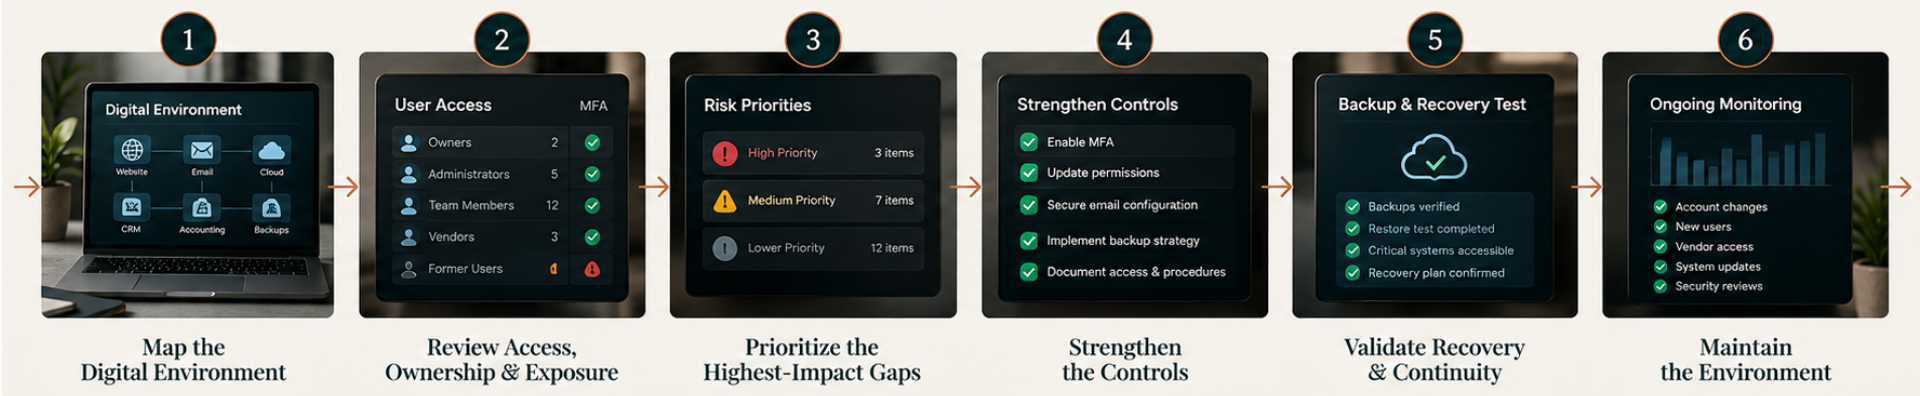
1. Map the Digital Environment
Identify the systems, accounts, vendors, users, devices, domains, email platforms, cloud services, websites, backups, and other digital dependencies the business relies on.
2. Review Access, Ownership & Exposure
Evaluate administrator access, user permissions, MFA, recovery methods, former-user access, vendor access, account ownership, and other conditions that can increase risk.
3. Prioritize the Highest-Impact Gaps
Separate urgent issues from lower-priority improvements so the business knows what needs attention first.
Priority is based on likelihood, business impact, recoverability, and how critical the affected system is to operations.
4. Strengthen the Controls
Implement practical improvements around access, authentication, email security, account configuration, backups, documentation, permissions, recovery, and other relevant controls.
5. Validate Recovery & Continuity
Confirm that the business can access critical systems, restore what needs to be restored, and continue operating if an account, vendor, device, or platform becomes unavailable.
6. Maintain the Environment
Review changes over time as employees, vendors, software, accounts, and business requirements evolve.
Security is not a one-time configuration. The digital environment changes with the business.
The goal is not perfect security. It is fewer avoidable weaknesses and a business that is better prepared when something goes wrong.
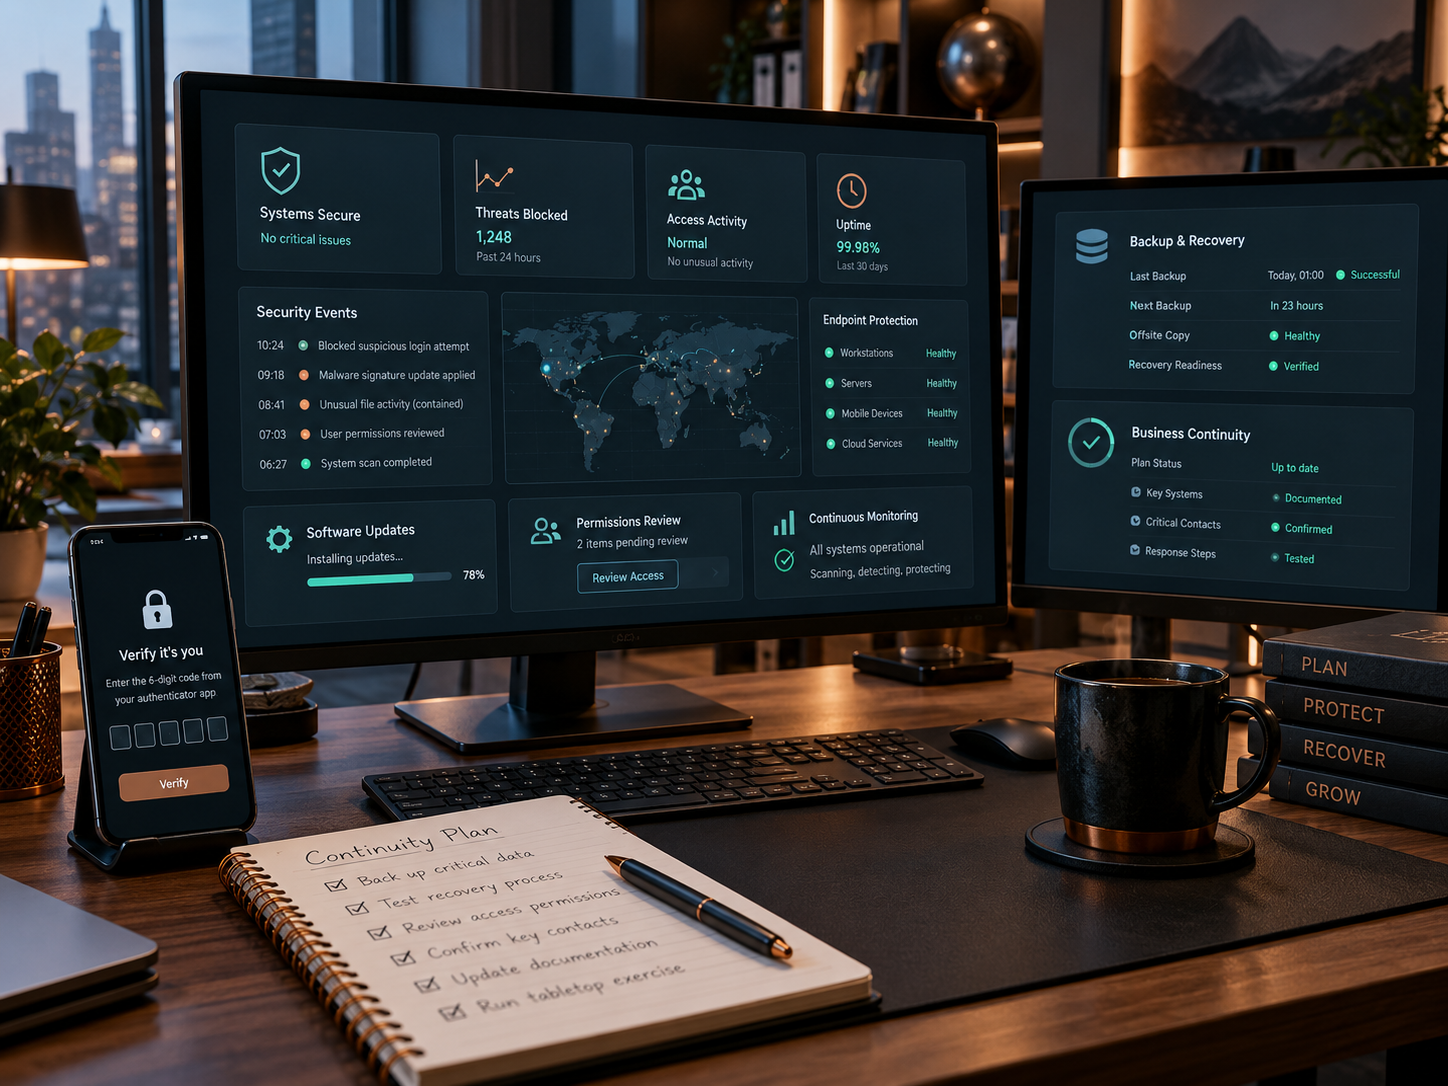
Cybersecurity starts with individual choices and becomes stronger when people, technology, and business continuity work together.
REDUCE RISK. IMPROVE READINESS.
Stronger security should help the business prevent, detect, respond, and recover.
Cybersecurity is not one product or one configuration.
A stronger security posture combines informed people, appropriate technology, ongoing monitoring, clear ownership, practical policies, and a realistic plan for what happens when something goes wrong.
What this can improve
Everyday security habits - Strengthen password practices, MFA adoption, software updates, phishing awareness, account recovery, and the basic behaviors that reduce common security failures.
Security visibility - Understand what protection is already in place, whether security tools are working as intended, and where alerts or gaps need attention.
Access & ownership control - Reduce unnecessary permissions and keep critical accounts and digital assets under clear business ownership.
Detection & monitoring - Improve visibility across security platforms, endpoint tools, email protection, backups, account activity, and other systems where early warning matters.
Business continuity - Prepare for outages, compromised accounts, unavailable vendors, lost devices, cyber incidents, and other disruptions so the business knows how to keep essential operations moving.
Recovery readiness - Maintain usable backups, documented recovery access, responsibilities, escalation paths, and tested procedures for restoring critical systems.
SECURITY IS AN ONGOING PRACTICE
Safer technology starts with informed people and consistent oversight.
Cybersecurity is not something a business configures once and considers finished.
People change. Software changes. Vendors change. New accounts are created. Permissions accumulate. Threats evolve. Security tools need review, updates, and attention to remain useful.
EmberNova Digital helps businesses build practical habits around security awareness, technology review, monitoring, and continuity so protection evolves with the business.
What that includes
Security awareness & everyday practices - Strengthen the basics that still matter: safer password habits, multi-factor authentication, software updates, phishing awareness, secure account recovery, and knowing when something should be questioned or reported.
Security software review - Review current endpoint protection, email security, backup tools, account protections, and other security platforms to identify gaps, overlap, weak configuration, or tools that are no longer serving the business well.
Ongoing monitoring - Establish a practical rhythm for reviewing alerts, security dashboards, backup health, user access, account activity, updates, and other indicators that deserve regular attention.
Employee & vendor lifecycle - Make access changes part of onboarding, role changes, offboarding, vendor transitions, and other moments when permissions can quietly become a risk.
Business continuity reviews - Revisit recovery plans, critical dependencies, escalation contacts, backup readiness, and operating priorities as the business grows or changes.
Security documentation - Keep policies, account ownership, recovery procedures, vendor information, access standards, and continuity plans current enough to be useful when they are actually needed.
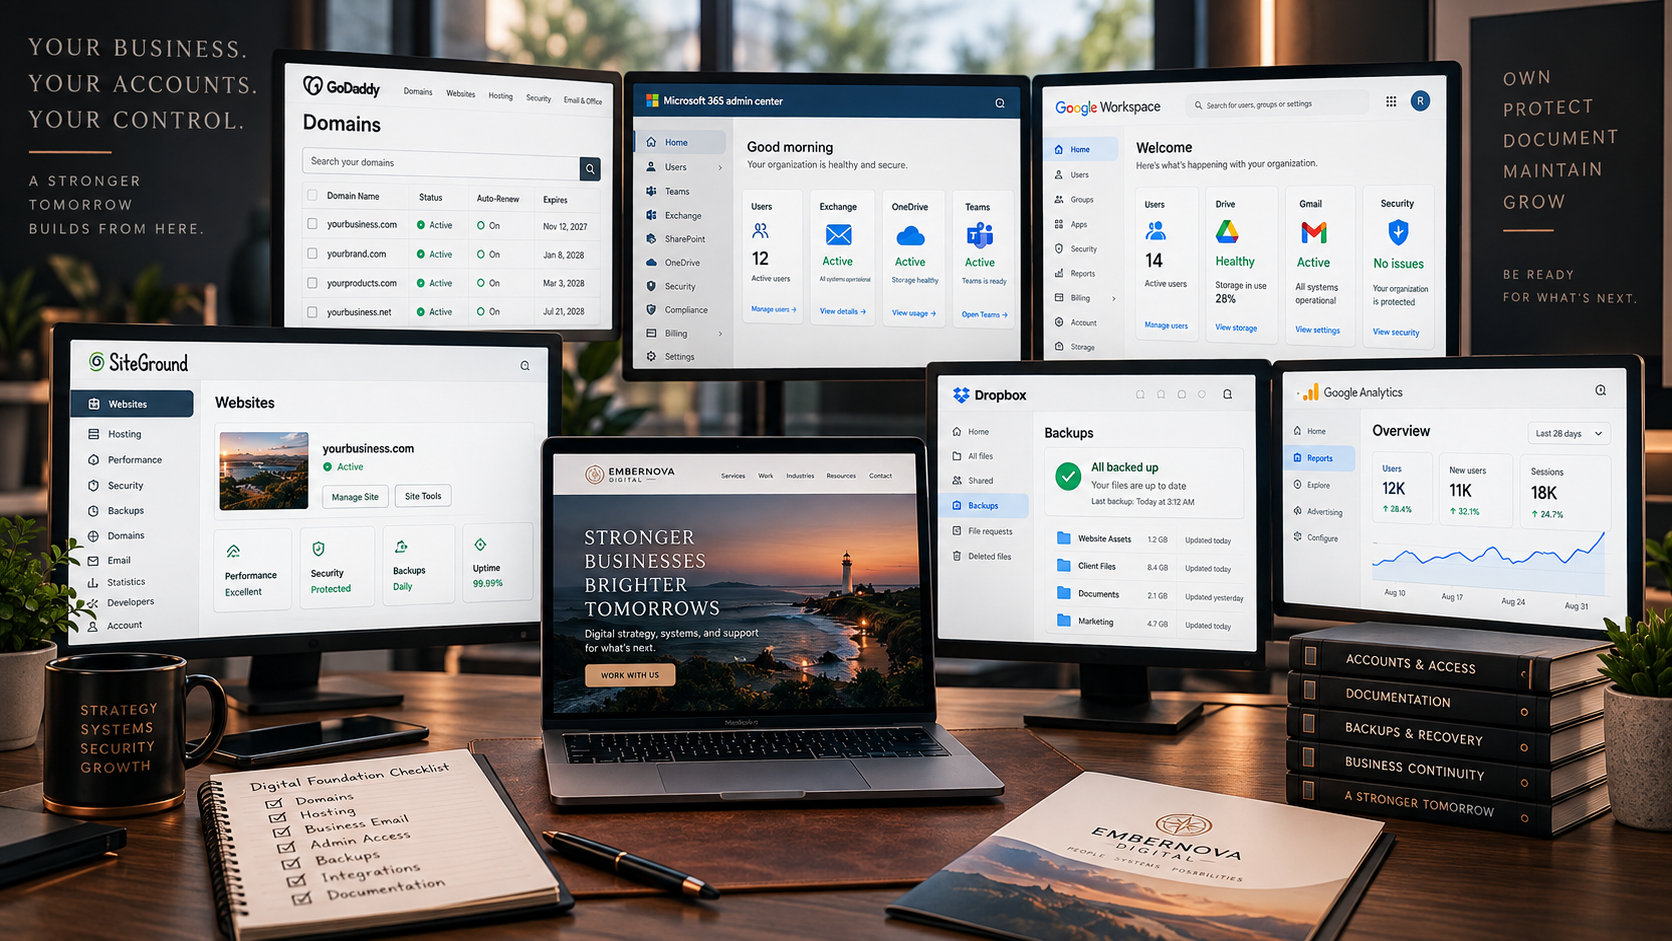
Cybersecurity starts with individual choices and becomes stronger through consistent habits, responsible technology, and preparation for what comes next.
PROFESSIONAL RESPONSIBILITY
Security should protect people, businesses, and the trust placed in technology.
As a member of the ISC2 Space Coast Chapter and an ISC2 Certified in Cybersecurity professional, Rachel Crow approaches cybersecurity with the same emphasis on responsibility, integrity, competence, and protecting the public interest that informs EmberNova Digital’s work across technology and AI.
For EmberNova Digital, security is not about creating fear or selling unnecessary complexity. It is about helping businesses make responsible decisions, reduce avoidable risk, and contribute to a safer digital environment.
Want your team to understand the risks, not just the rules?
EmberNova Digital can provide practical cybersecurity workshops for business owners and teams, including foundational security awareness, safer day-to-day habits, and current threat patterns employees should know how to recognize.
Available for private teams, associations, chambers, workshops, and educational events.
REAL RESILIENCE WORK
Security matters most when the business can keep operating through change, failure, or disruption.
Cybersecurity and resilience work often becomes visible at the worst possible moment: a compromised website, lost access, an unstable hosting environment, or a critical system that no longer has a clear owner.
The better outcome is to identify those weaknesses earlier and build stronger recovery, access, ownership, and continuity into the business before they become emergencies.
WordPress Malware & Fake reCAPTCHA Compromise
Investigated and remediated a compromised WordPress environment involving fake CAPTCHA-style malware, injected code, a rogue plugin, a malicious must-use plugin, and unauthorized administrator access. The work included removing malicious persistence, cleaning injected code, reviewing users and plugins, clearing caches, rescanning the environment, and documenting follow-up hardening steps.
Malware Remediation · Incident Response · Access Review · WordPress Security
Microsoft 365 Email Authentication & Deliverability Remediation
Investigated a business email deliverability issue involving an Intermedia-managed Microsoft 365 environment, unclear administrative control, and incomplete authentication. The work included reviewing tenant ownership and access, SPF/DKIM/DMARC configuration, DNS, forwarding, and email policy conditions, then enabling DKIM and validating the corrected configuration.
Microsoft 365 · Email Security · DNS · Authentication · Ownership
Business Continuity & Digital Infrastructure Recovery
Recovered and stabilized compromised or fragile digital environments where website access, hosting, domains, backups, account ownership, or vendor dependencies created operational risk. Work has included restoring control, rebuilding infrastructure, clarifying ownership, and strengthening recovery readiness.
Business Continuity · Digital Recovery · Ownership · Resilience
The visible website is only one part of the work. The real value is building the digital environment around it well.
Featured in Best of Florida
The Business That Runs Itself
A closer look at why stronger systems, clearer ownership, and reduced founder dependency matter as businesses grow, transition, and prepare for what comes next.
COMMON QUESTIONS
Cybersecurity works best when risk, recovery, and day-to-day operations are considered together.
Every business has a different mix of people, systems, vendors, access, and operational dependencies. These questions cover the areas owners and leadership teams most often need clarified before deciding what kind of security or resilience work makes sense.
What does a cybersecurity risk assessment include?
A practical assessment can review critical systems, user access, account ownership, email security, backups, recovery options, security tools, vendor dependencies, continuity risks, and other conditions that affect the business’s ability to prevent, detect, respond, and recover.
Do you review the security software we already use?
Yes. EmberNova Digital can review endpoint protection, email security, backup tools, account protections, monitoring platforms, and other existing controls to identify gaps, unnecessary overlap, weak configuration, or tools that are no longer serving the business well.
Can you help with ongoing security monitoring?
Yes. Support can include reviewing security dashboards, backup health, account activity, user access, alerts, updates, and other recurring indicators that deserve consistent attention.
Do you help with business continuity planning?
Yes. Business continuity work can include identifying critical systems and dependencies, documenting recovery priorities, clarifying responsibilities, reviewing backup readiness, establishing escalation paths, and planning how essential operations continue during disruption.
Is cybersecurity mostly a technology issue?
No. People are a major part of security. Strong passwords, multi-factor authentication, regular software updates, phishing awareness, secure account recovery, and knowing when to report suspicious activity are basic controls that still matter.
Can you help after a website, email account, or digital system has already been compromised?
Yes. Depending on the situation, EmberNova Digital can help investigate, recover access, remediate malicious changes, review permissions and ownership, restore systems, and identify the follow-up steps needed to reduce the chance of recurrence. Urgent incidents should use the Emergency Digital Recovery pathway.
Do you provide cybersecurity policies or employee guidance?
Yes. Practical documentation can include password and MFA standards, access rules, vendor practices, employee onboarding and offboarding, incident reporting, recovery procedures, and other recurring security situations.
How often should security and continuity plans be reviewed?
They should be revisited whenever the business, team, vendors, software, or critical systems change, and on a regular schedule even when nothing appears wrong. Security environments drift over time.
STRENGTHEN THE BUSINESS BEFORE THE NEXT PROBLEM